
 de
Data Handling Policy
Everyone who handles personal data for Babylon Berlin follows these rules: employees, the fulfilment partner Acut, and the web agency navus. They cover the online shop babylonberlin.shop and all marketplace sales, including Amazon.
- Data covered: customer and buyer data, order and invoice data, account and system access data.
- Systems covered: the WooCommerce shop and its database, backups, the Babylon PIM plugin (marketplace connection), email, and any export or printout.
- Amazon buyer data also falls under Amazon’s Data Protection Policy. Where Amazon’s rules are stricter than GDPR, Amazon’s rules apply.
- Policy owner: the data protection contact named by Babylon Berlin.
1.1 Classification
All data falls into one of four levels; personal data of customers and Amazon buyers is always Confidential.
| Level | Examples | Rule |
|---|---|---|
| Strictly confidential | API keys and refresh tokens (Amazon, eBay, Kaufland, OTTO), admin passwords, payment provider keys | Only in the shop settings or a password manager. Never sent by email or chat. Changed after a staff change or an incident. |
| Confidential | Names, addresses, phone numbers, email addresses (incl. Amazon relay addresses), order contents, invoices | Only for people who need it for the order. Never copied into spreadsheets, chats or email bodies. Deleted on schedule (1.4). |
| Internal | Stock levels, sales figures, supplier terms, sync logs without personal data | Staff, Acut and navus only. |
| Public | Product data, prices, published texts and legal pages | May be shared freely. |
Card data is never stored by Babylon Berlin; payments run through the payment provider.
1.2 Access
People see personal data only when their task needs it, through their own account with two-factor login.
| Who | May access | How |
|---|---|---|
| Babylon Berlin staff | Orders, customer data, invoices | Personal shop account (Shop Manager), two-factor login |
| Acut (fulfilment) | Orders and delivery addresses, only to ship | Own account or API key limited to orders and shipments; removed when the contract ends |
| Navus, UAB (web agency) | Shop administration; personal data only to fix a reported problem | Personal admin accounts, two-factor login |
| Seller Central users | Amazon orders | Personal Amazon logins with two-step verification |
- No shared accounts or passwords.
- Access is removed on the day someone leaves or a contract ends.
- Accounts and API keys are reviewed every 6 months.
- Two-factor login in the shop runs through Wordfence Login Security.
1.3 Storage, encryption and transfer
Personal data lives only in the shop database, its backups and the marketplaces’ own systems; it is encrypted at rest and only travels over encrypted connections.
- Where: the WooCommerce database at the hosting provider (EU), its backups, and Seller Central. No copies on laptops, USB sticks, spreadsheets or chat tools.
- At rest: database and backup storage encrypted with at least AES-128 (Amazon’s minimum). Open: the hosting provider confirms this in writing.
- In transit: HTTPS with TLS 1.2 or higher for the shop, the admin area and all marketplace APIs; email is sent over TLS.
- Logs: system and sync logs record order numbers and statuses only, never names, addresses, phone numbers or emails.
- Paper: packing slips with addresses are destroyed after shipping.
1.4 Retention and deletion
Amazon buyer data is anonymised automatically no later than 30 days after delivery; only what tax law requires is kept longer.
| Data | Kept for | Then |
|---|---|---|
| Amazon and other marketplace buyer data in orders (name, street, phone, email) | Until 30 days after delivery | Anonymised automatically by a daily job; city, postcode and country stay for tax |
| Invoices and accounting records | Statutory period under HGB and AO (currently up to 10 years) | Deleted |
| Shop customer data | As long as the order, customer account or a legal duty requires | Deleted or anonymised |
| Backups | Overwritten after at most 30 days (open: confirm the hosting backup cycle) | Overwritten |
| Sync logs (no personal data) | 30 days | Deleted automatically |
1.5 Processing records and partners
The existing record of processing activities (Art. 30 GDPR) gets one new entry, “Marketplace order fulfilment (Amazon)”, and every partner with access to buyer data has a contract that covers it.
New entry in the record:
- Data: buyer name, delivery address, phone, Amazon relay email, order contents, invoice data.
- Purpose and legal basis: fulfilling the order and invoicing it (Art. 6(1)(b) GDPR); tax duties (Art. 6(1)(c) GDPR).
- Recipients: Acut, the shipping carrier, the hosting provider, navus.
- Retention and security: as in 1.3 and 1.4 of this policy.
| Partner | Role | Agreement |
|---|---|---|
| Dogado | Processor | Data processing agreement (Art. 28 GDPR) |
| Acut | Processor (fulfilment) | Data processing agreement |
| Navus, UAB | Processor (web agency) | Data processing agreement |
| SMTP | Processor | Data processing agreement |
| DHL or other carrier | Own controller | Carrier terms |
| Amazon | Own controller | Amazon seller agreement and Data Protection Policy |
1.6 Security incidents
Anyone who notices a possible incident — a lost laptop or phone, an unknown login, data sent to the wrong person — reports it at once; when Amazon buyer data is involved, Amazon is told within 24 hours.
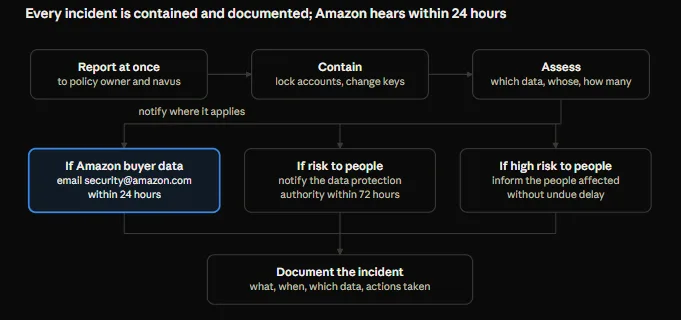
Every incident is documented, even when nothing has to be reported. The authority is the one for the company’s seat (Berlin or Brandenburg; open: which).
1.7 Responsibilities and review
The policy owner keeps this policy, the processing record and the partner agreements current, and reviews them every year.
- Before access: everyone reads this policy and confirms it in writing; Acut and navus confirm it for their staff.
- Every year: a short refresher for everyone with access.
- Extra reviews: after any incident, a new partner, or a new marketplace.